Your Developers Are Pasting Company Code Into Public AI Tools
And your legal team probably has no idea. Why casual AI prompts create data risks, and three guardrails teams can use without giving up the tools.
By Emmanuel Itighise
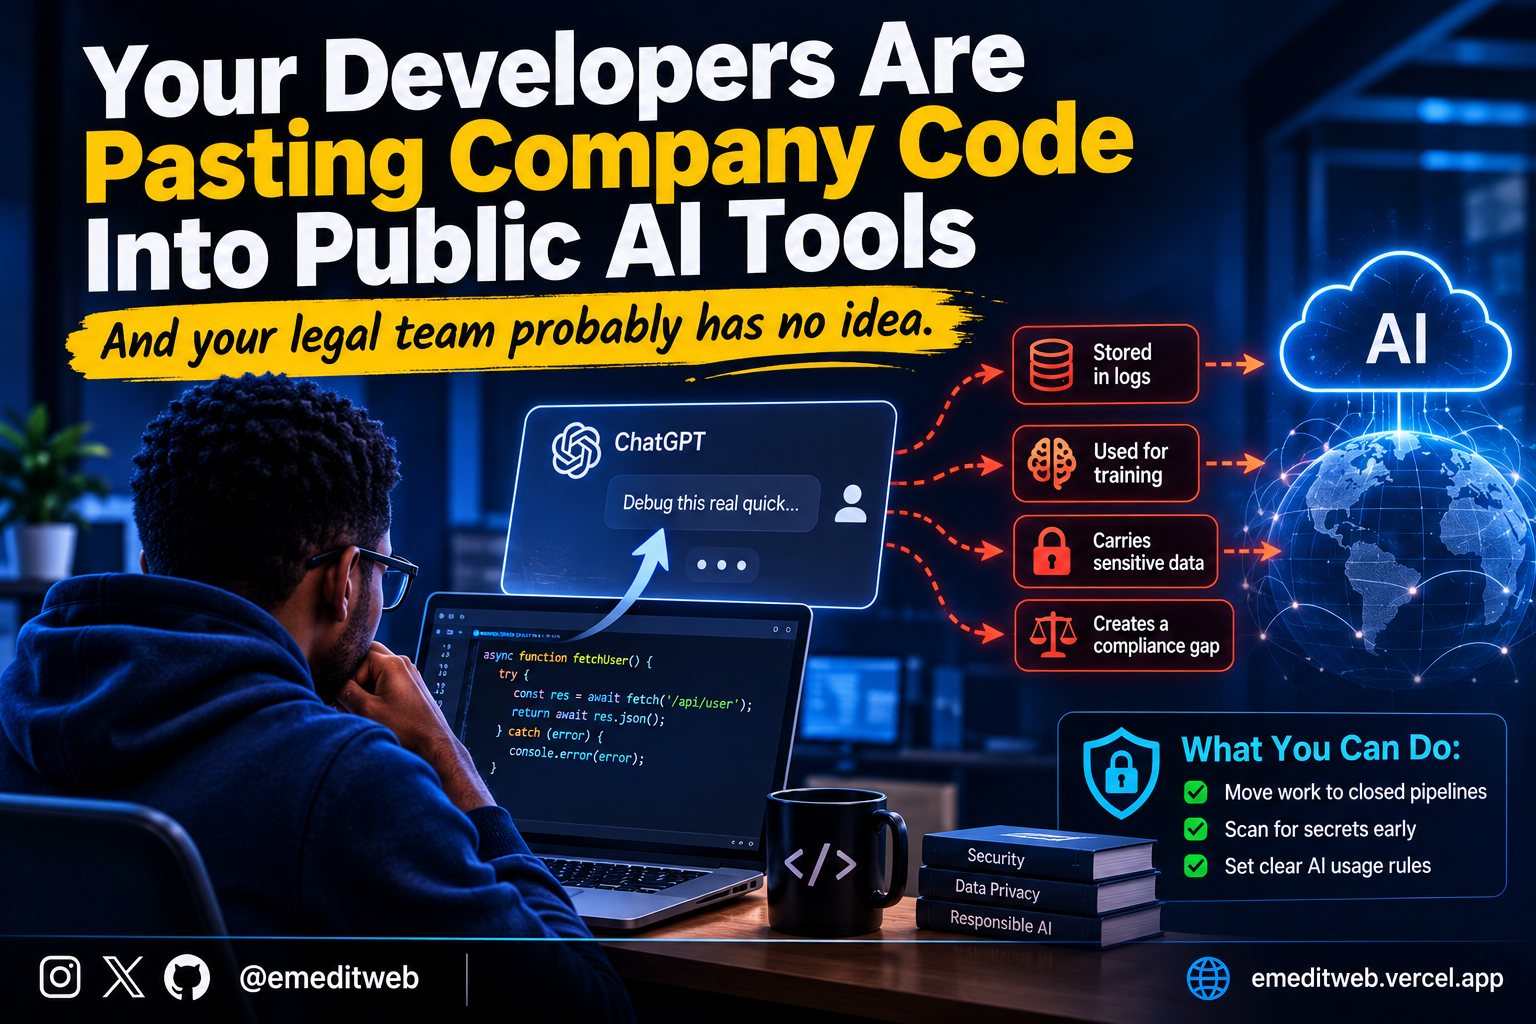
And your legal team probably has no idea.
It usually starts small. A developer hits a bug in a backend handler, or in an auth flow that hasn’t shipped yet. They paste it into an AI chat and write “debug this real quick.” It works, so tomorrow they do it again, and soon the whole team does.
I’m an AI-native developer, so I’m not here to say stop using these tools. I use them every day. But I’ve seen how casually code gets pasted into a prompt, and I think most companies haven’t caught up with what that means.
What actually goes wrong
Once code leaves your systems, you no longer control where it goes. Here is what that can mean in practice:
- It can be stored. Prompts can sit in provider logs, and sometimes in the user’s chat history for months, depending on the service and its retention settings.
- It can be used for training. This depends on the plan and the settings. Many consumer tools allow opt-outs, and business plans often exclude training on your data by default, but a developer using a personal account may never check.
- It can carry more than code. A pasted snippet often includes client data, internal URLs, API keys or database credentials that nobody meant to share.
- It creates a compliance gap. If that code includes personal data, sharing it can trigger obligations under laws such as the NDPA 2023 or GDPR, where applicable, and nobody wrote down where the data went.
This has happened at real companies. In 2023, Samsung reportedly restricted staff use of ChatGPT after engineers pasted internal source code into it. If a company with that many lawyers and security staff can be caught out, a startup or mid-sized firm certainly can.
Why banning it doesn’t work
The obvious answer is to block the tools. I don’t think it works. Developers who feel slowed down will use a personal phone or laptop, and now you have the same risk with less visibility. Banning removes your control instead of adding it.
The better answer is to give people a safe way to do what they’re already doing.
Three guardrails you can set up now
1. Move work to closed pipelines
Use approved business or enterprise plans with contractual controls over training and retention. Where available and appropriate, arrange zero data retention for eligible API endpoints; don’t assume every enterprise plan includes it. Route developer tools through your own API gateway to enforce access rules and logging policies, while checking what the upstream provider retains. If the code is sensitive enough, run an open-weight model such as Llama inside your private cloud, with external access and telemetry controlled so the code stays inside your network.
2. Scan for secrets early
Be clear about what this does. A Git hook or CI check can’t stop someone pasting into a chat window. What it can do is catch keys, credentials and configured sensitive patterns before they reach a repository or are merged, which matters because IDE plugins and coding assistants read repository files. Pair it with a simple written rule: secrets never go into prompts.
3. Decide what AI is allowed to touch
Write it down. AI can help with small utility functions, test generation and boilerplate. Core architecture, authentication flows and anything security-sensitive stays human-designed and human-reviewed. This keeps the speed where it’s safe and the judgment where it matters.
Where the job is heading
For a long time, being a good engineer meant writing good code. That’s still true, but now there’s a second half: knowing where code and data came from, and where they went. Senior engineers and technical leads will spend more of their time on audit and provenance, and less on typing.
Companies that set clear rules now will move faster later, because their teams won’t have to guess what’s allowed. Companies that wait will find out about the problem from a client, a regulator or a leak.
Innovation without governance is a liability waiting to happen.
How does your team balance speed with protecting company data? I’d like to hear what’s working for you.
References
About the author

Emmanuel Itighise
Founder of Stepfi-App, @Pulsar-Stellar/sdk, and Trybe.
Emmanuel Itighise, known online as Emeditweb, is a full-stack and AI-native developer based in Lagos, Nigeria. He builds practical products and developer tools, with a focus on web applications, AI, and the Stellar ecosystem. He shares lessons from building in public, contributing to open source, and turning ideas into working software.